Behind the Firewall: How Enterprise Security Teams Are Engineering Proprietary Face-Swap Detection Systems

Photo by Photo by Winston Chen on Unsplash on Unsplash
The public narrative around AI face-swapping technology tends to focus on creative applications — film production, virtual influencers, interactive media. But inside enterprise security operations centers across the United States, a quieter and considerably more consequential conversation is taking place. Corporate security teams are confronting a straightforward but uncomfortable reality: the consumer-grade detection tools available on the open market were not designed to operate at organizational scale, under adversarial conditions, or against the latest generation of synthesis models. As a result, a growing cohort of enterprises is diverting significant engineering resources toward building proprietary detection infrastructure entirely in-house.
Understanding why that shift is happening — and how developers can replicate the underlying architecture — requires a clear-eyed look at both the threat model and the technical limitations of existing public tools.
Why Consumer Detection Tools Fall Short in Enterprise Environments
Popular open-source and commercially available deepfake detectors were largely trained on benchmark datasets such as FaceForensics++ and the Deepfake Detection Challenge corpus. These datasets, while valuable for academic benchmarking, reflect a specific historical window of synthesis techniques. Modern face-swap models have advanced substantially beyond the artifacts those detectors were calibrated to identify.
More critically, consumer tools are static. They are trained once, released, and updated on a cadence that cannot realistically track the pace of generative model development. An enterprise deploying one of these tools in a high-stakes verification pipeline — executive identity confirmation, financial authorization, secure video conferencing — is effectively relying on a detection surface that adversaries can study, probe, and systematically circumvent.
Enterprise environments also introduce scale requirements that consumer tools simply cannot satisfy. A financial institution processing thousands of video verification sessions daily needs detection latency measured in milliseconds, not seconds. It needs audit trails, integration with existing identity and access management systems, and the ability to flag edge cases for human review without interrupting the primary workflow. None of that comes standard.
The Architecture of an Internal Detection Pipeline
Enterprise-grade detection systems typically decompose the problem into several discrete, independently scalable components. Developers building these systems should think in terms of a layered pipeline rather than a single monolithic classifier.
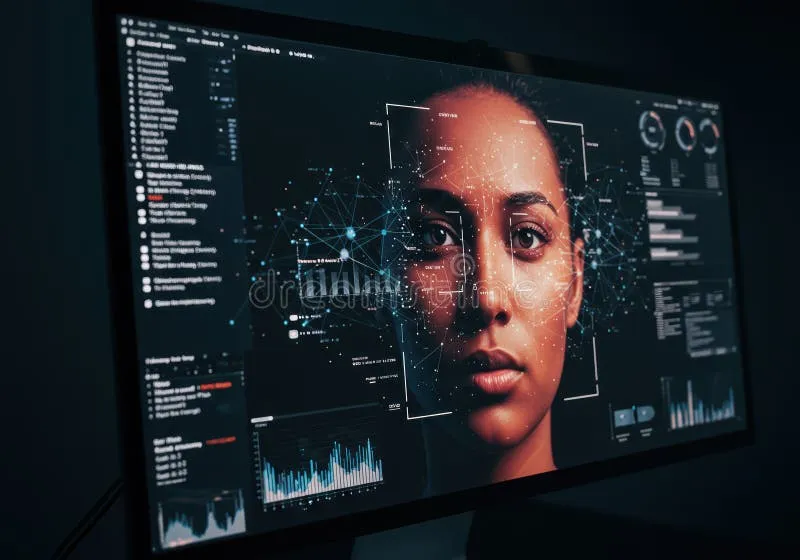
Frame-level forensic analysis forms the first layer. At this stage, individual video frames are passed through convolutional neural networks trained to identify spatial inconsistencies — unnatural skin texture gradients, lighting discontinuities at facial boundaries, and compression artifact patterns that differ from genuine video. This layer operates at high throughput and is designed to flag candidates for deeper analysis rather than render final verdicts.
Temporal coherence analysis constitutes the second layer, and it is where many consumer tools fail entirely. Authentic human faces exhibit predictable micro-movement patterns across frames — subtle muscular contractions, natural blinking cadence, consistent head pose trajectories. Current face-swap models, despite their visual fidelity, often produce temporal inconsistencies that are imperceptible frame-by-frame but statistically detectable when analyzed across sequences. Recurrent architectures, particularly those incorporating 3D convolutional layers or transformer-based temporal attention mechanisms, have demonstrated meaningful accuracy improvements on this dimension.
Behavioral biometric cross-referencing represents a third layer that more sophisticated enterprise deployments are beginning to incorporate. Rather than evaluating video in isolation, these systems compare real-time facial movement patterns against enrolled behavioral baselines for known individuals. Deviations from established patterns — even subtle ones — trigger elevated scrutiny. This approach shifts the detection problem from purely forensic to identity-anchored, which substantially raises the bar for adversarial circumvention.
The Adversarial Feedback Loop
Any honest treatment of enterprise detection engineering must acknowledge the fundamental tension at the center of this problem. Detection models improve; generation models adapt. The cycle is well-documented in academic literature and is playing out with increasing velocity in commercial contexts.
One mechanism enterprises are using to address this is continuous adversarial retraining. Internal red teams generate synthetic face-swap content using the latest available models — including fine-tuned variants and custom-trained architectures — and inject that content into the training pipeline for the detection system on a regular cadence. This is resource-intensive, but it produces detectors that are meaningfully more robust against contemporary synthesis techniques than anything trained on static public datasets.
A complementary approach involves ensemble detection, in which outputs from multiple independently trained classifiers are aggregated before a final determination is rendered. Because different models exhibit different failure modes, an ensemble is considerably harder to fool simultaneously than any single detector. The tradeoff is computational overhead, which requires careful infrastructure planning — particularly for deployments that must maintain low latency at scale.
Integration Considerations for Developers
Developers tasked with building or extending internal detection systems should prioritize several architectural decisions early in the design process.
First, data governance and retention policies must be established before any biometric data touches the pipeline. Video verification inherently involves the processing of biometric information, and US state-level regulations — including Illinois's Biometric Information Privacy Act and analogous frameworks in Texas and Washington — impose specific requirements around collection notice, consent, and data retention limits. Detection infrastructure that is not designed with compliance in mind from the outset will require costly remediation.
Second, model versioning and rollback capability is not optional. Detection models will need to be updated as the threat landscape evolves, and the ability to roll back to a prior version when a new model introduces unexpected false positive rates is operationally essential. Treating detection models with the same rigor as production software — including versioned artifacts, staged rollouts, and automated performance regression testing — is a discipline that distinguishes mature internal programs from ad hoc implementations.
Third, developers should design explicitly for human-in-the-loop escalation. No automated detection system operating at enterprise scale will achieve zero false positives or false negatives. The pipeline should route borderline cases to a review queue staffed by trained analysts, and that review workflow should feed back into the model retraining process. The human layer is not a concession to imperfect technology; it is a structural component of a well-designed system.
What the Enterprise Shift Signals for the Broader Ecosystem
The movement toward proprietary internal detection infrastructure reflects a broader maturation in how organizations are thinking about AI-generated synthetic media as an operational risk category. Face-swap technology is no longer a novelty that security teams can afford to monitor at a distance. It is a credible vector for executive impersonation, financial fraud, and access control circumvention — and the organizations that recognize that earliest are investing accordingly.
For developers working in this space, the enterprise security context offers a technically demanding but instructive proving ground. The engineering constraints — adversarial robustness, latency requirements, compliance obligations, and the need for continuous adaptation — push detection systems toward architectural patterns that are genuinely more rigorous than what the consumer application context demands.
The arms race framing is accurate, but it can be misleading if it implies stasis. Enterprises that invest in adaptive, continuously retrained, behaviorally anchored detection infrastructure are not merely keeping pace — they are building systems that impose meaningful costs on adversaries and reduce organizational exposure in ways that static consumer tools cannot approach.